Monitor
Scan code, repositories, images and serverless packages with Trivy while maintaining an updated SBOM of the software in each running workload, including changes made after the build.
Explore MonitorRank each vulnerability by what production evidence shows, so teams can route it to the right owner and protect the workload until the fix ships.
Scan code, repositories, images and serverless packages with Trivy while maintaining an updated SBOM of the software in each running workload, including changes made after the build.
Explore MonitorRank vulnerabilities by EPSS, CISA KEV, network exposure and whether the affected workload is running, so teams start with what is exposed in production.
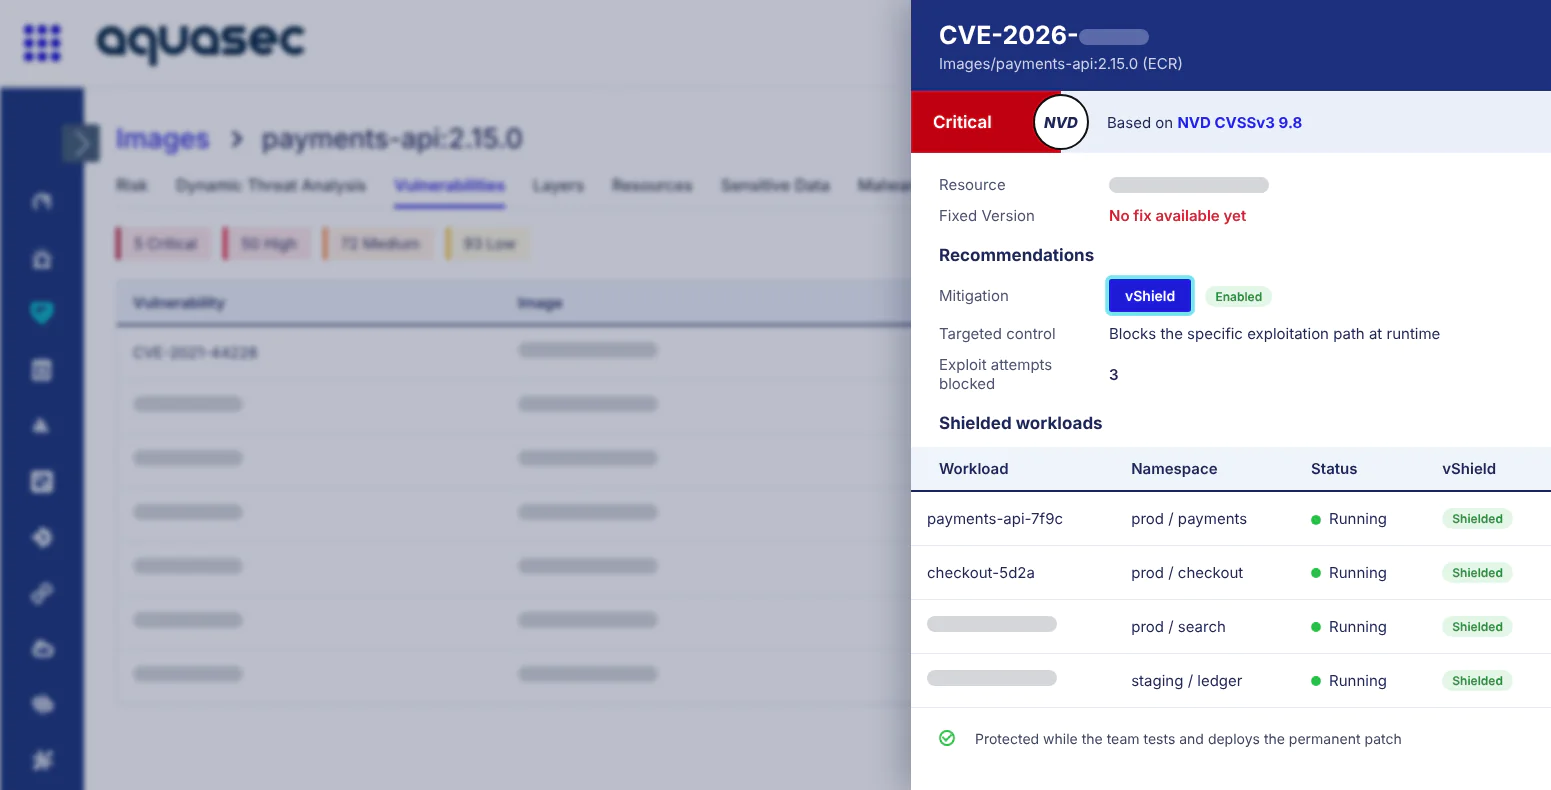
Explore DetectBlock supported exploitation paths at runtime with vShield, a targeted compensating control that protects the workload while teams test and deploy a permanent patch.
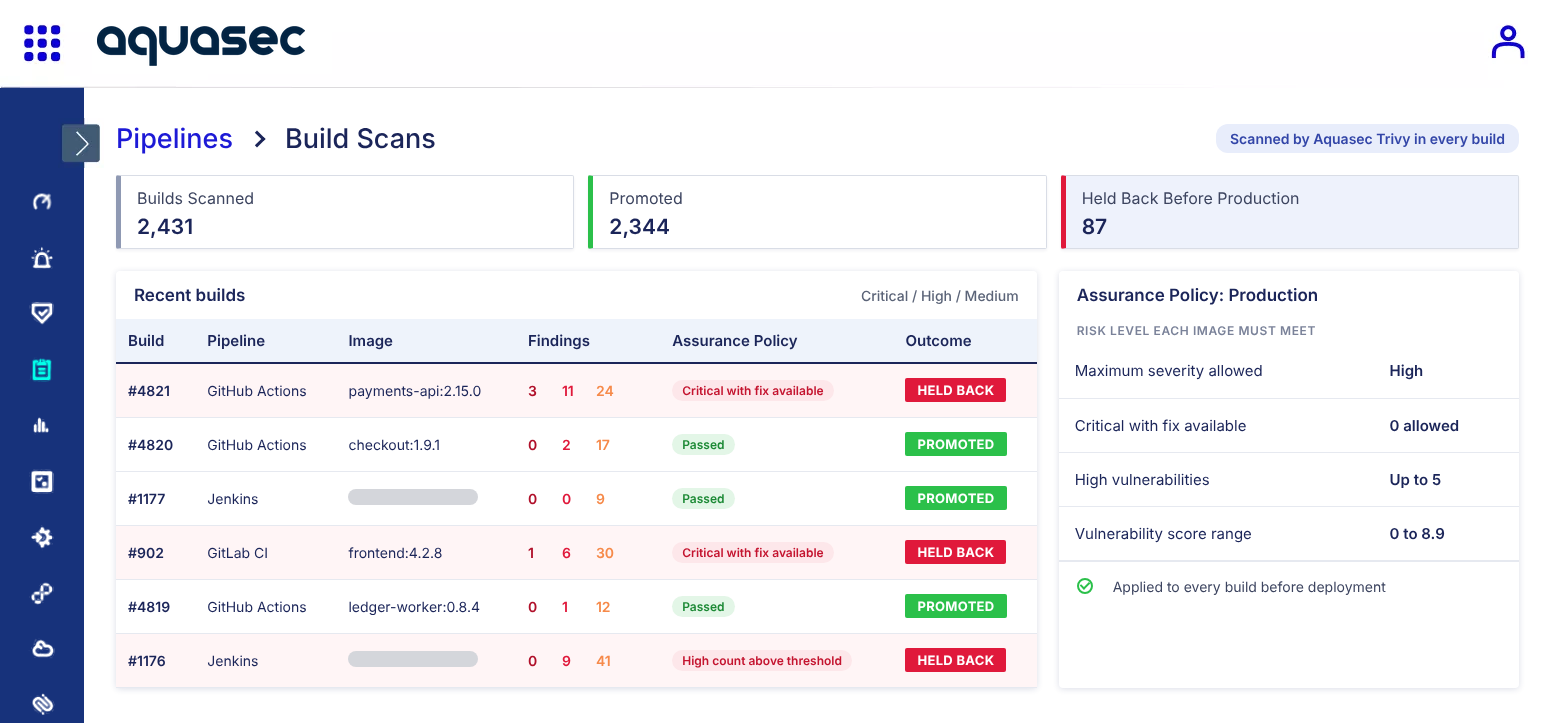
Explore EnforceHold risky images back before they reach production. Aquasec Trivy scans every build in CI/CD, and Assurance Policies define the risk level each image must meet before deployment.
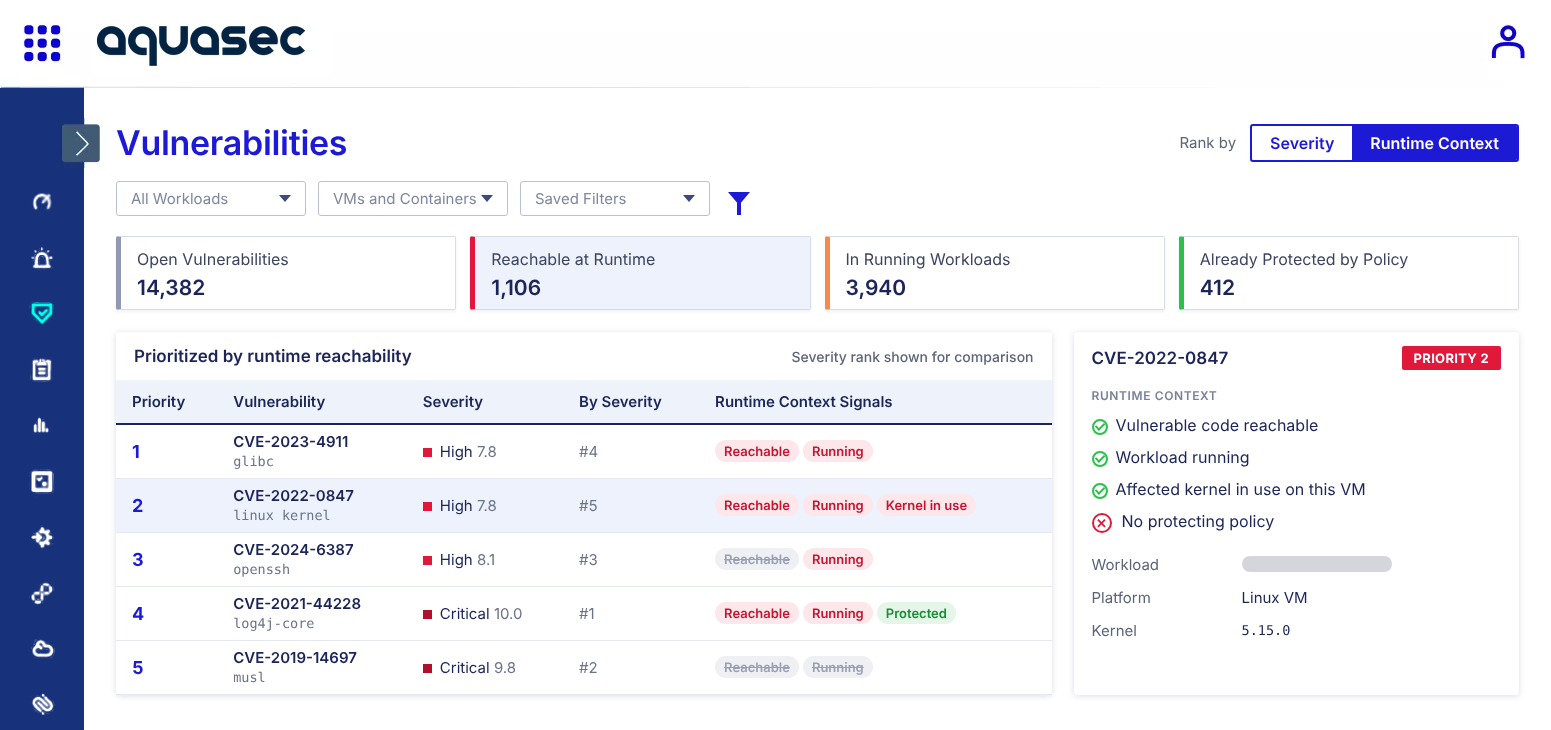
Rank vulnerabilities by what is happening inside the running workload, not by severity scores alone. Runtime Context weighs runtime reachability signals, whether the workload is running, the kernel in use on supported Linux VMs and the policies protecting it.
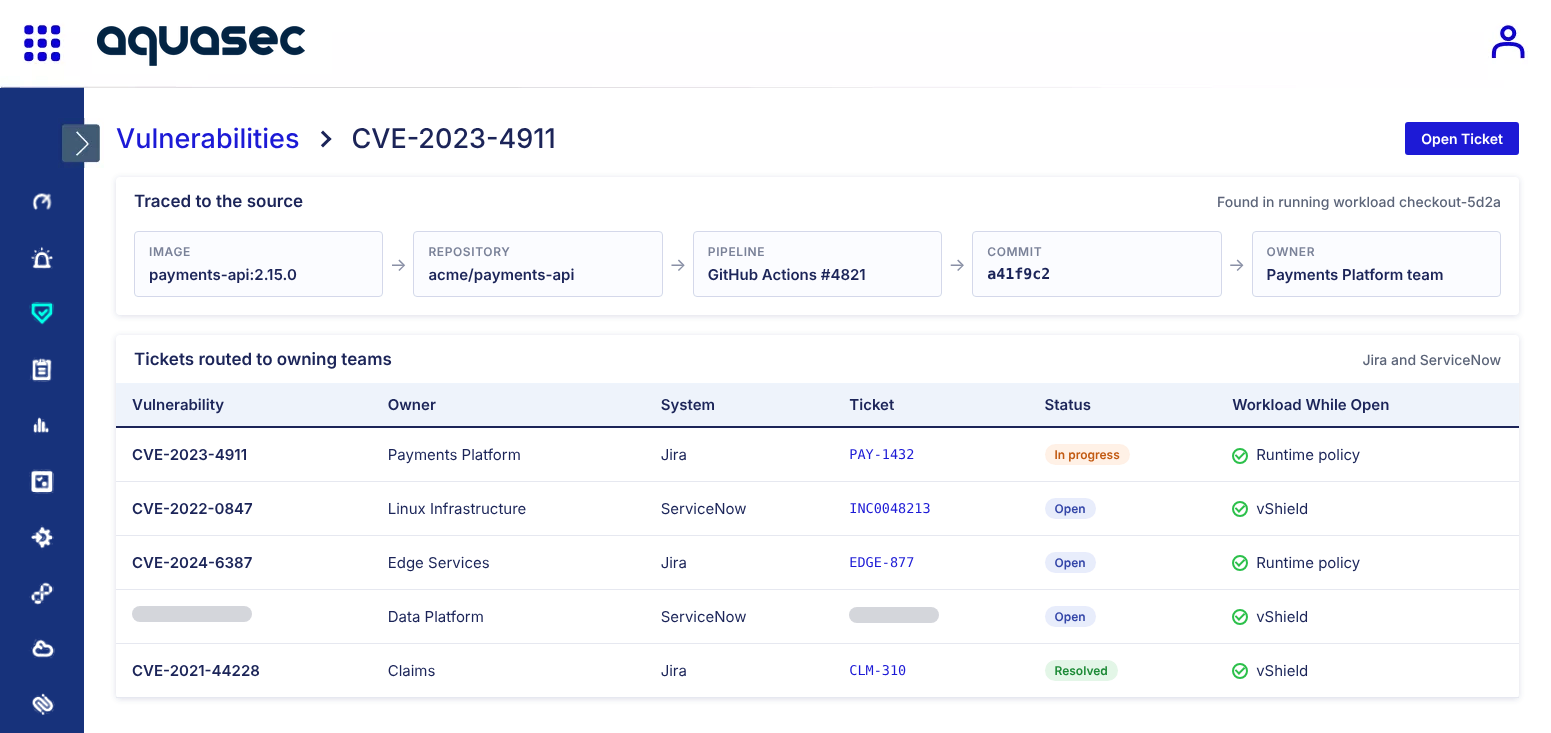
Route every finding to the team that can fix the source. Aquasec traces each vulnerability back to its image, repository, pipeline, commit and owner, then opens tickets in Jira or ServiceNow while the workload stays protected.
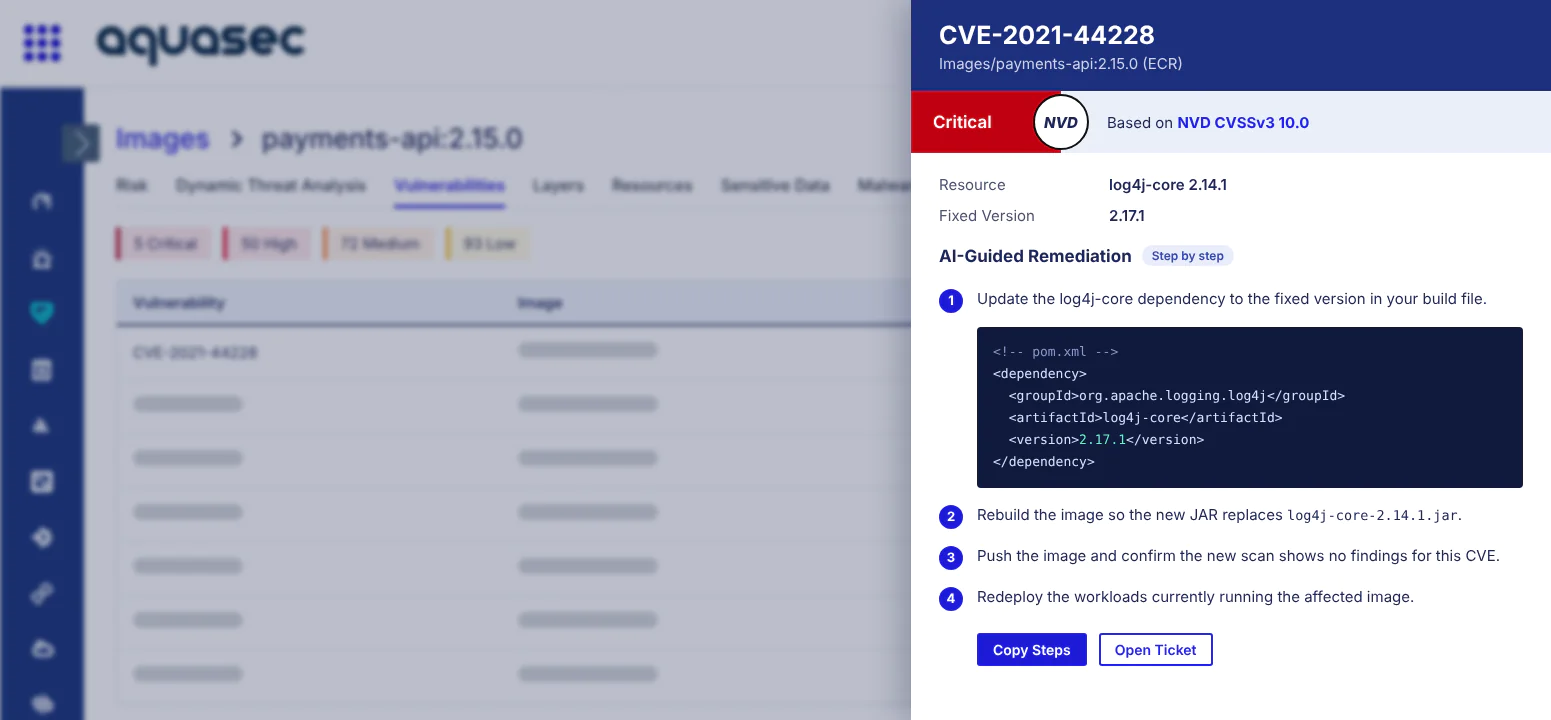
Shorten time to resolution without researching advisories and patches by hand. AI-Guided Remediation turns each vulnerability or misconfiguration into clear, step-by-step instructions for completing the fix, available throughout the Aquasec Platform interface.
Protect workloads from vulnerabilities that have no fix yet. vShield applies a targeted control to the specific exploitation path at runtime while teams test and deploy the permanent patch.
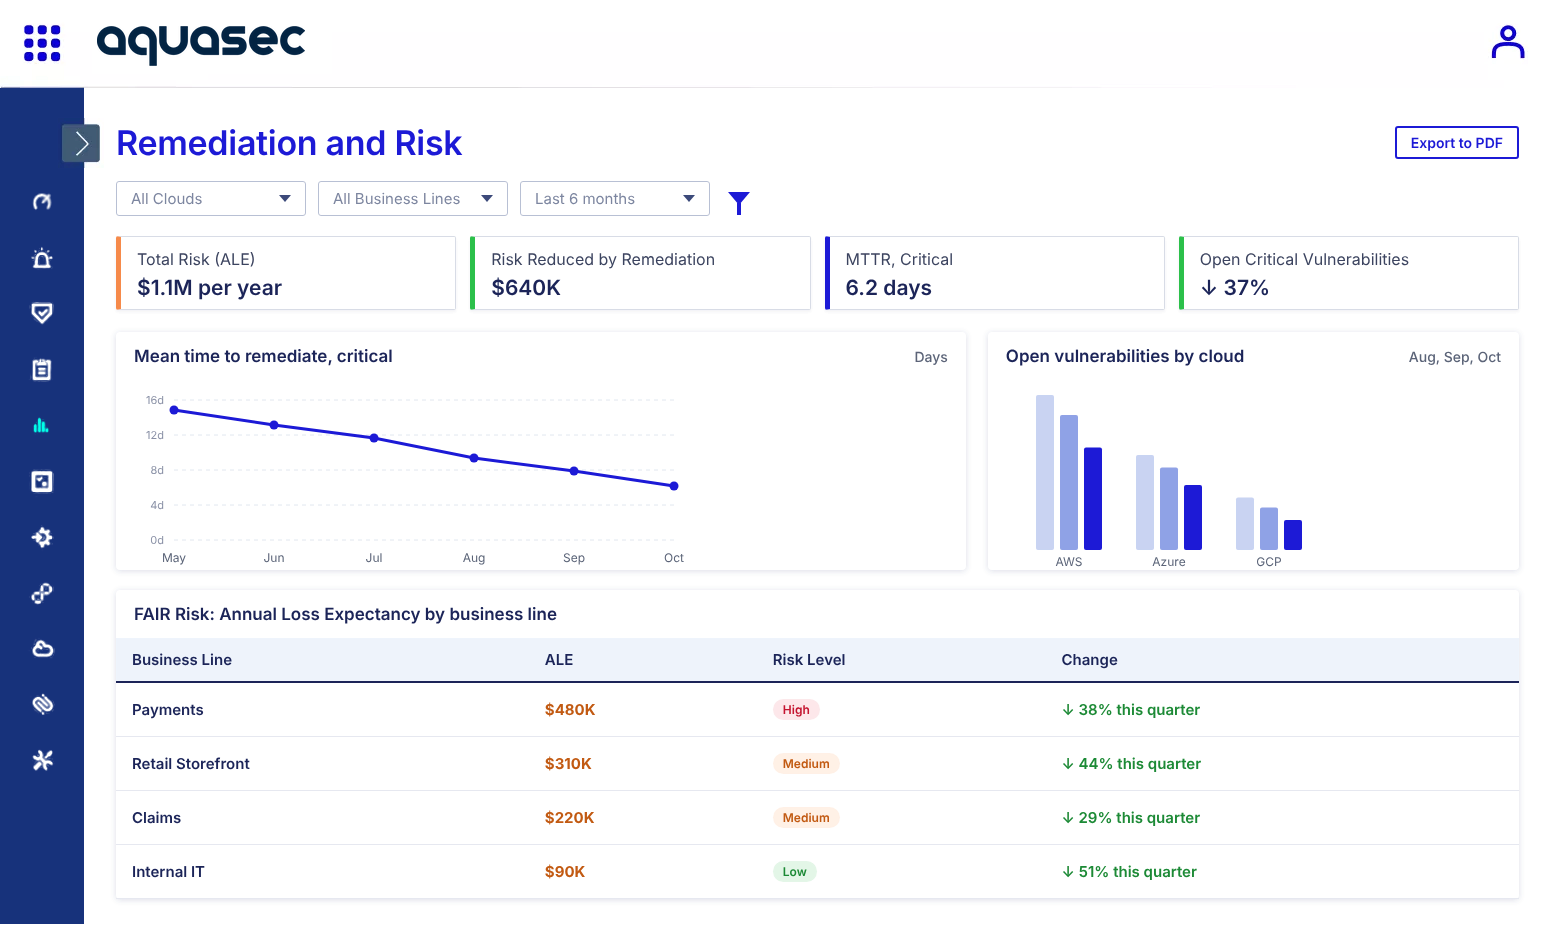
Show leadership how remediation reduces risk. Teams track MTTR and vulnerability trends across clouds, and the FAIR Risk Dashboard converts exposure into Annual Loss Expectancy for each business line
Aquasec scans the systems your teams use to build and store software, then routes findings into the workflow tools they use to fix it, in SaaS or fully self hosted deployments.
 JFrog Artifactory
Continuously scan container images in Artifactory for known vulnerabilities, embedded secrets, OSS licenses, malware, and configuration issues.
 Jenkins
Automate container image scanning in Jenkins CI/CD pipelines to empower DevOps to detect and fix security issues early, and accelerate application deployment.
Learn More
 ServiceNow
Orchestrate incident management responses based on Aqua Security findings with automated ServiceNow integration. Leverage Aqua Response Policies for event notifications to direct and manage via ServiceNow workflows.
Learn More
 Atlassian Jira
Automatically open tickets for vulnerabilities and security issues discovered by Aqua, to enable rapid remediation by DevOps teams.
Learn More
 Amazon ECR
Continuously scan container images in Amazon ECR for known vulnerabilities, embedded secrets, OSS licenses, malware, and configuration issues.
 GitLab
Automate container image scanning in GitLab CI/CD pipelines to empower DevOps to detect and fix security issues early, and accelerate application deployment.
Read the GitLab Case Study
 Azure DevOps
Scan images and functions directly in Azure DevOps CI/CD pipelines to empower DevOps to detect and fix security issues early, and accelerate application deployment.
Get Aqua for Azure DevOps
 Red Hat Quay
Continuously scan container images in Red Hat Quay for known vulnerabilities, embedded secrets, OSS licenses, malware, and configuration issues.
 Harbor
Continuously scan container images in Harbor for known vulnerabilities, embedded secrets, OSS licenses, malware, and configuration issues.
Cloud native vulnerability management finds and resolves vulnerabilities across code, images, registries and running workloads instead of treating each scan in isolation. Aquasec adds runtime context to decide what comes first and applies compensating controls with vShield when a fix cannot ship right away.
Severity scores rate a vulnerability in isolation. Aquasec weighs runtime reachability signals, whether the affected workload is running, the kernel in use on supported Linux VMs and the policies already protecting it, so teams can tell a theoretical finding from real exposure in production.
vShield is Aquasec’s virtual patching capability. It applies a targeted runtime control to the exploitation path of a known vulnerability, which reduces exposure while teams test and deploy a permanent fix. It is a compensating control, not a substitute for patching.
Aquasec Trivy is the open source scanning foundation for vulnerability, misconfiguration, secret, license and SBOM analysis. The Aquasec Platform adds centralized management, enterprise intelligence, policy, prioritization, remediation workflows and connection to runtime controls.
Aquasec traces each finding to the image, repository, commit and owner involved and opens tickets in Jira or ServiceNow. In the SaaS edition, AI-Guided Remediation adds step-by-step instructions for completing each fix.
See runtime control stop an attack the moment it tries to execute.