Detect
Surface toxic combinations where a misconfiguration, an exposed service, an excessive permission or a vulnerable image meets a running workload, so teams fix the risk an attacker could actually use.
Explore DetectAquasec treats cloud and Kubernetes configuration as context for the applications running on it, so each finding is prioritized and reported based on what it actually exposes in production.
Surface toxic combinations where a misconfiguration, an exposed service, an excessive permission or a vulnerable image meets a running workload, so teams fix the risk an attacker could actually use.
Explore DetectDeny noncompliant pods at admission with KubeEnforcer, using built-in best practices and custom OPA Rego rules based on pod, namespace, node and cluster attributes.
Explore EnforceMap cloud, Kubernetes, host and identity configuration to CIS Benchmarks, NIST, PCI DSS, HIPAA, GDPR, SOC 2 and FedRAMP, and show controls operating in production rather than checked once.
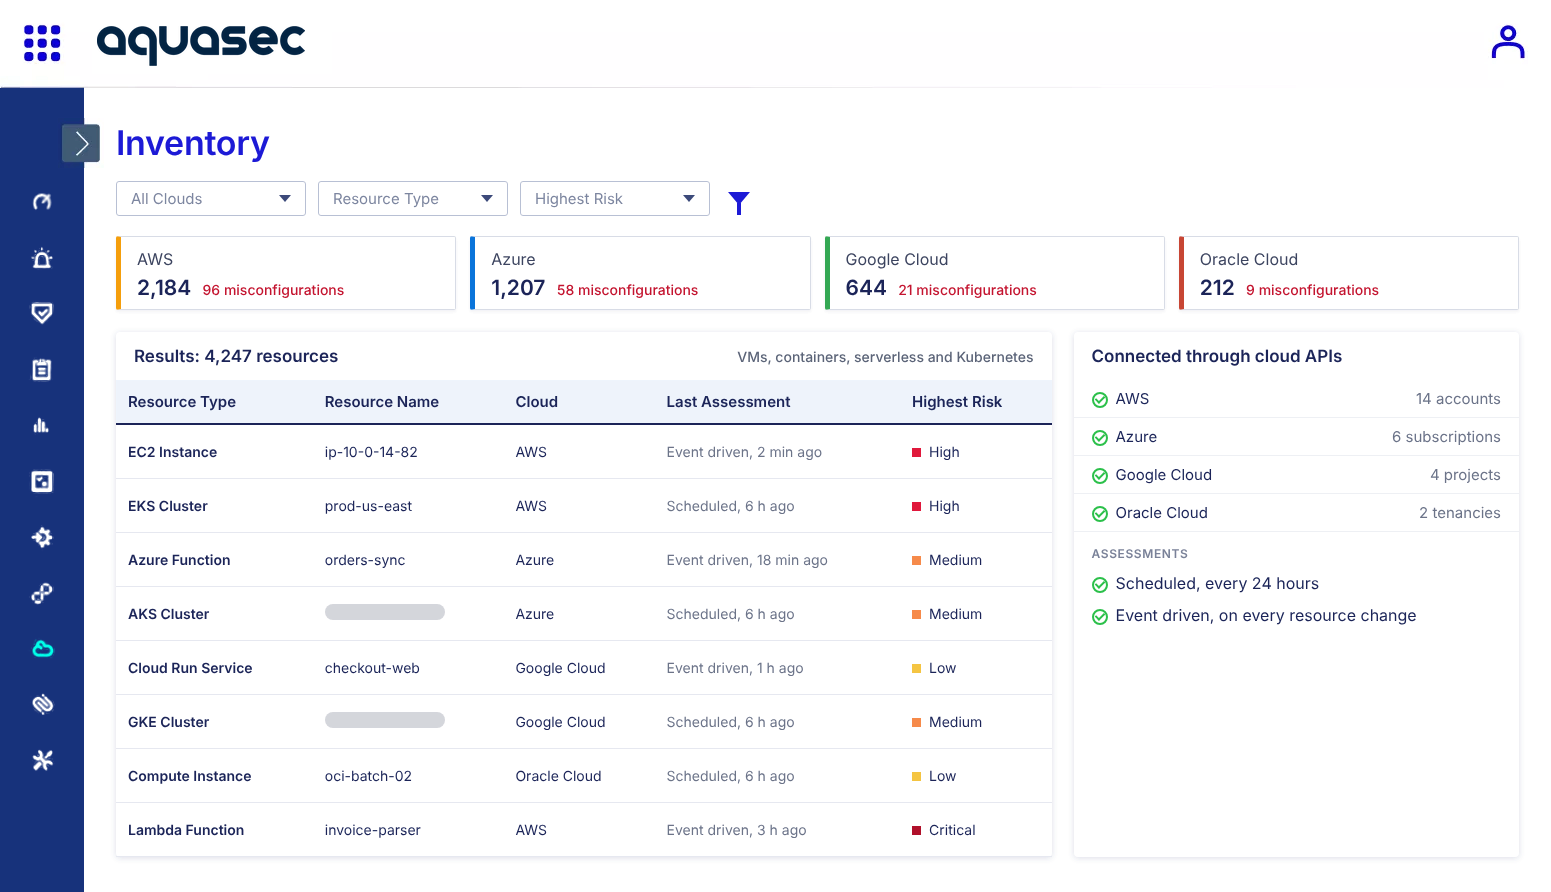
Explore ComplianceFind misconfigurations across AWS, Azure, Google Cloud and Oracle Cloud Infrastructure from a single view. Aqua connects through cloud provider APIs, maps VMs, containers, serverless functions and Kubernetes clusters, and runs both scheduled and event driven assessments.
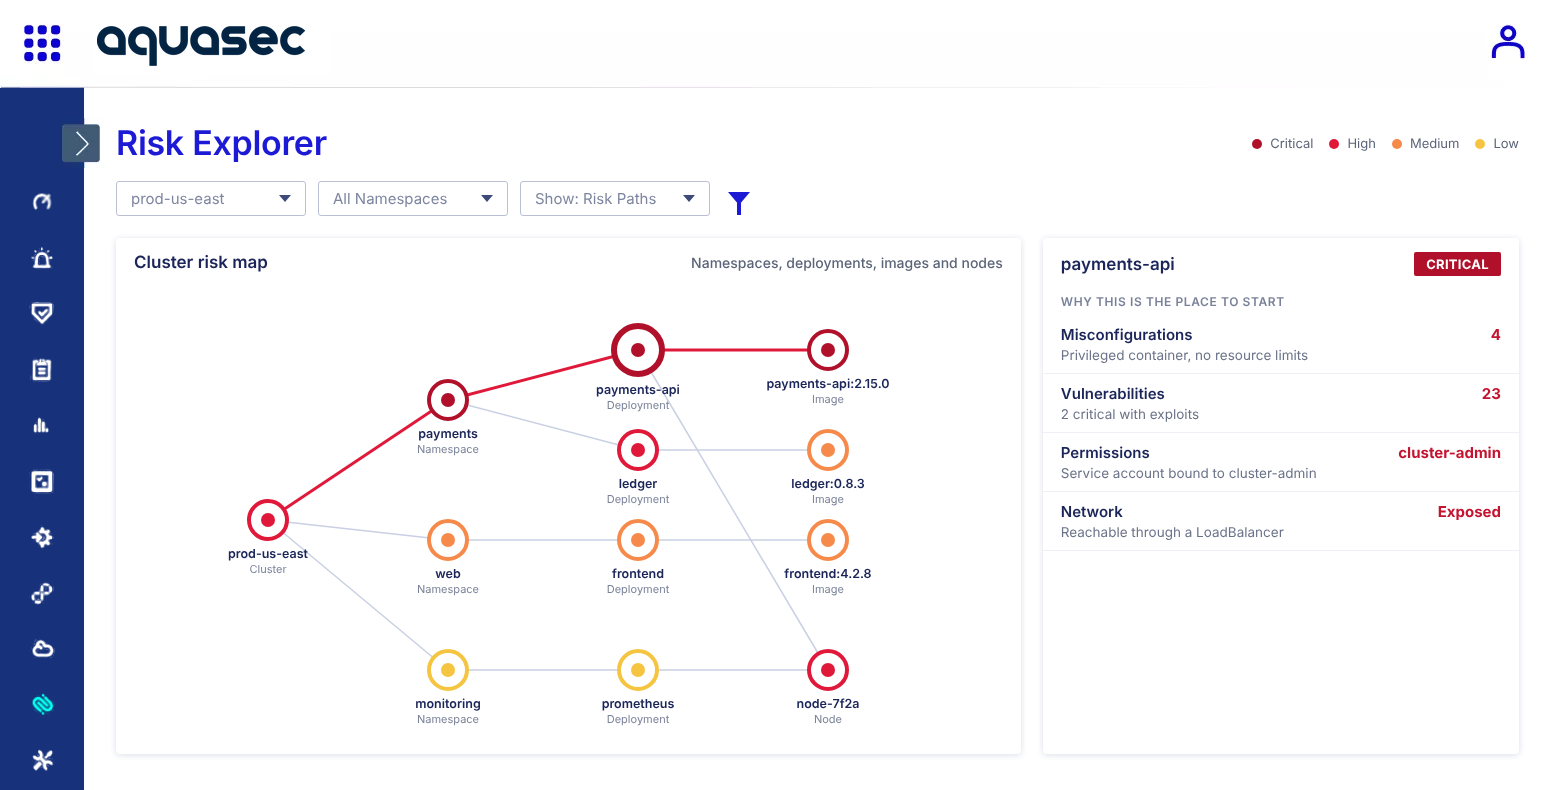
See how misconfigurations, vulnerabilities, permissions and network connections combine inside each cluster. Risk Explorer maps namespaces, deployments, nodes and images and rates the risk of each so teams know where to start.
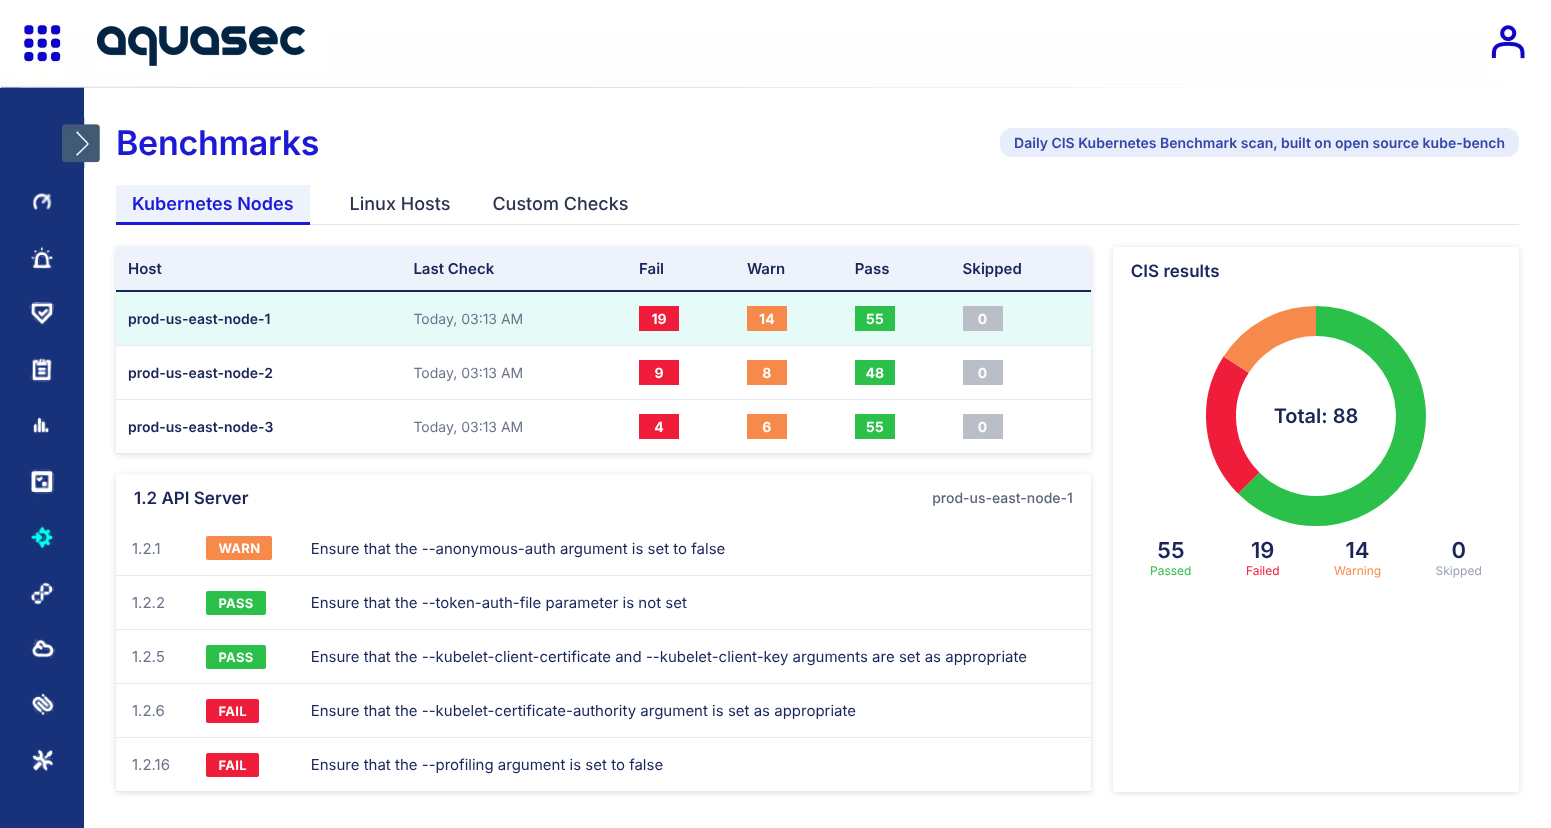
Check Kubernetes clusters and Linux hosts against CIS Benchmarks automatically. Aqua runs daily CIS Kubernetes Benchmark scans built on kube-bench, its open source project, and assesses hosts against CIS hardening guidance.
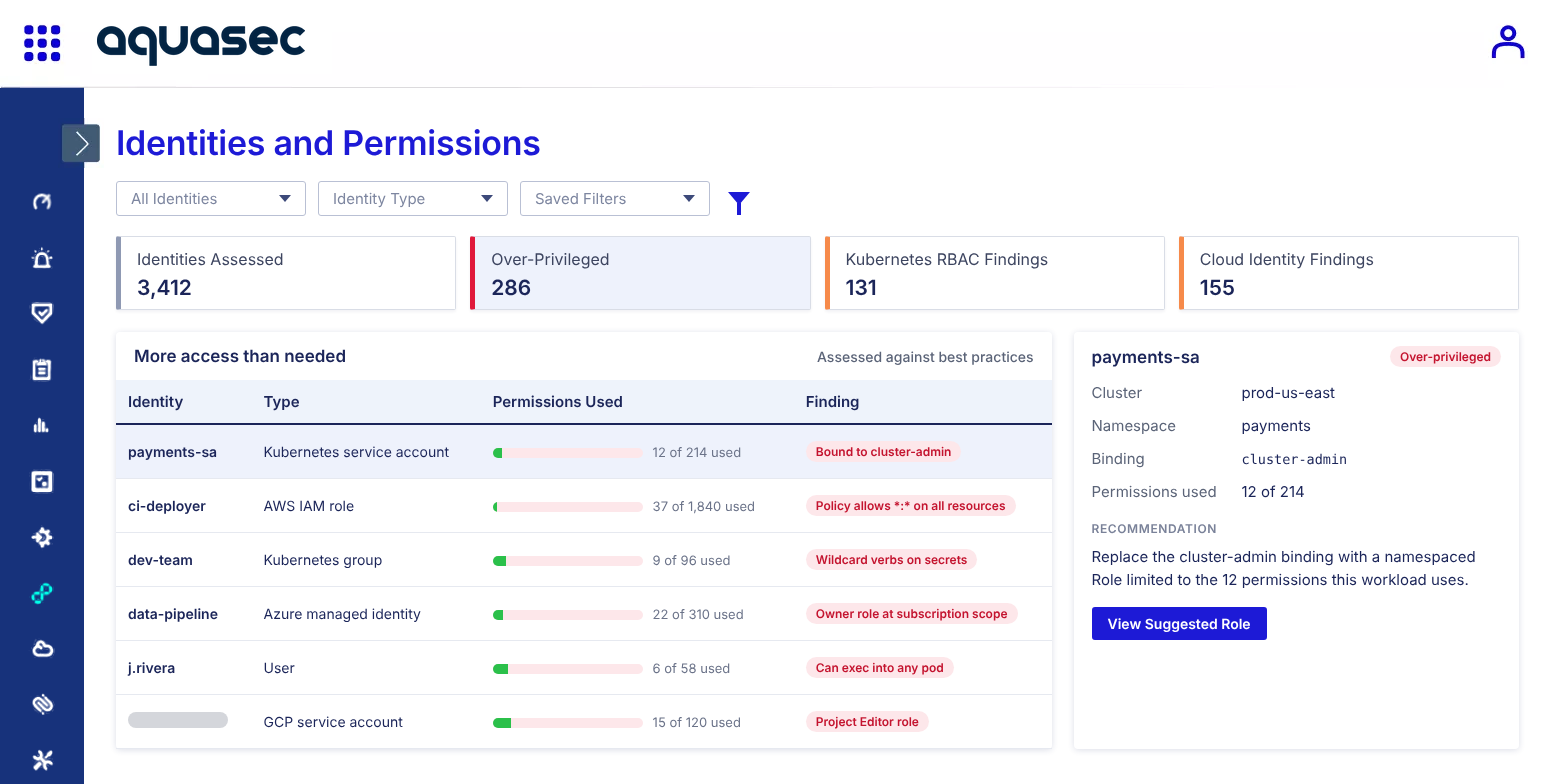
Find the users, service accounts, roles and cloud identities with more access than they need. Aqua assesses Kubernetes RBAC and cloud identity permissions against best practices and highlights where privileges can be reduced.
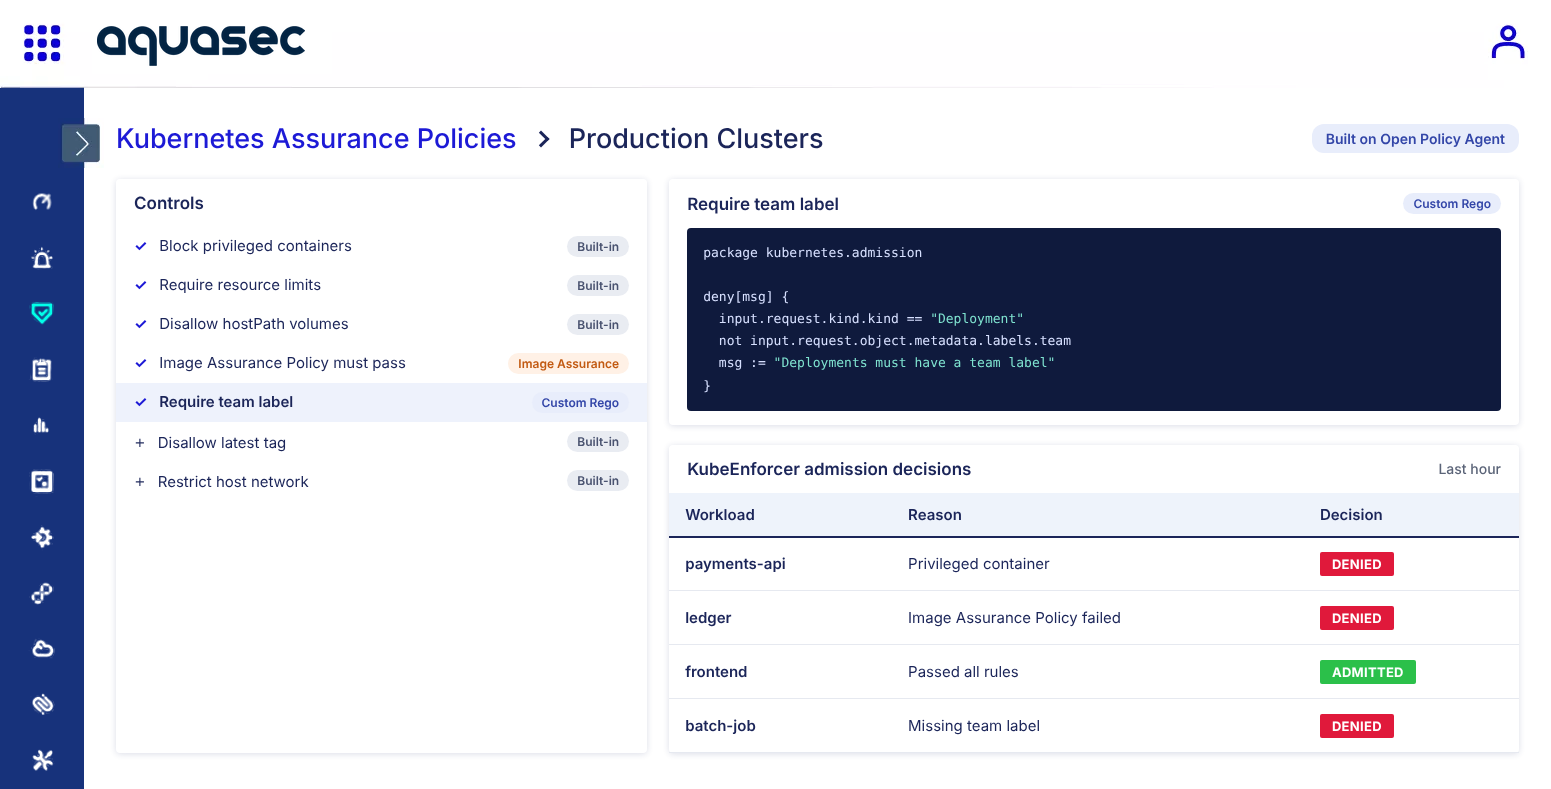
Stop workloads that fail policy from starting in the cluster. Kubernetes Assurance Policies built on Open Policy Agent combine built-in rules, custom Rego and Image Assurance Policy results to decide what KubeEnforcer admits.
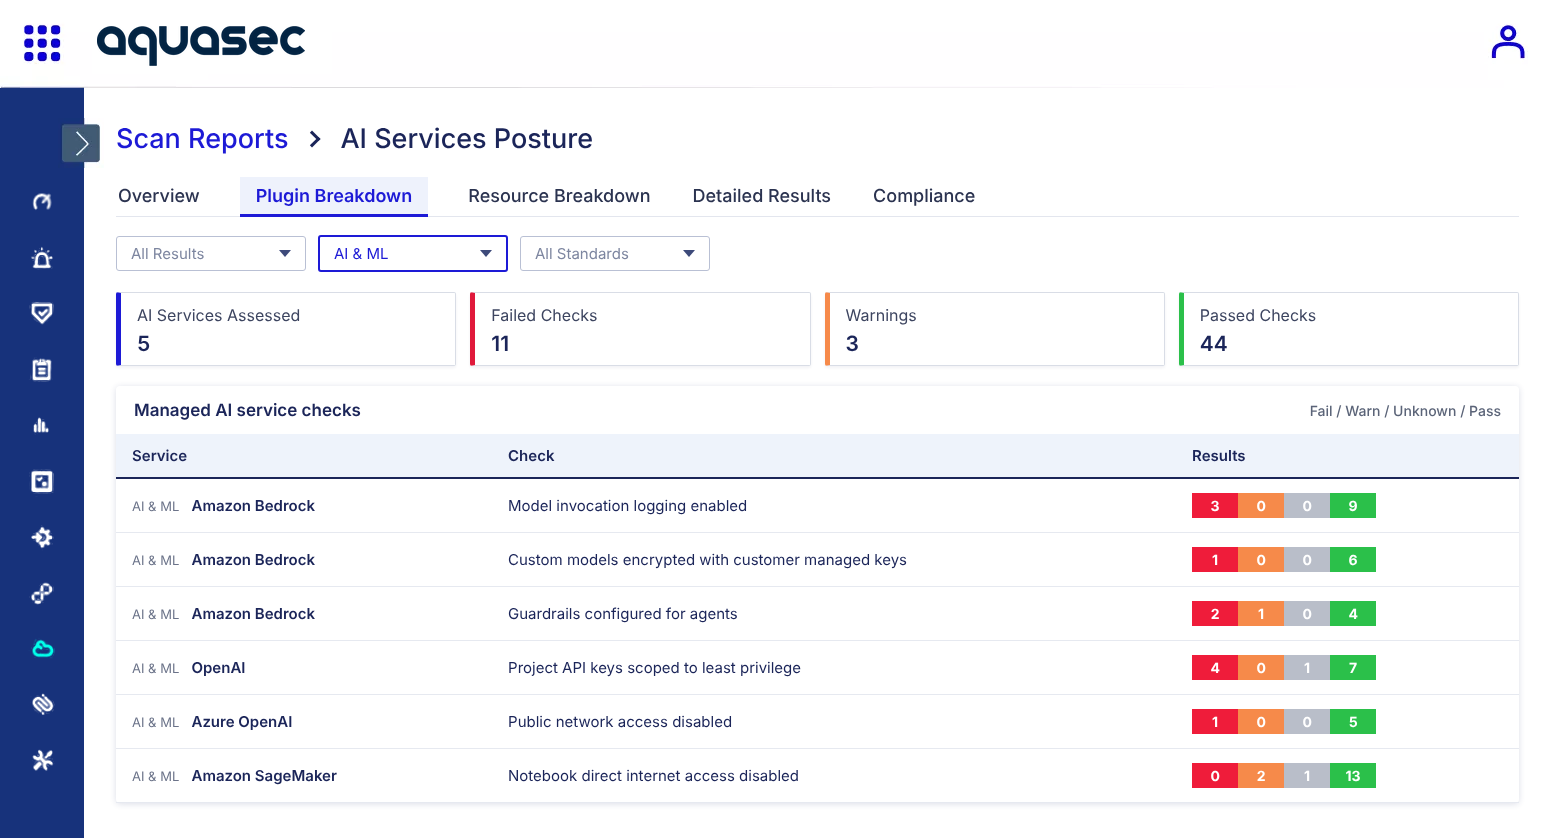
Extend posture checks to the managed AI services your teams adopt. AI-SPM assesses services such as OpenAI and Amazon Bedrock against governance standards to reduce misconfiguration risk.
Aquasec connects to cloud provider APIs and Kubernetes clusters across public cloud, private cloud, hybrid and on premises environments, then routes findings to the tools teams use to fix them.
 Amazon Web Services
Protect cloud native workloads running on AWS from development to production, including Amazon ECS, Amazon EKS, AWS Fargate, and AWS Lambda.
Get Aqua from AWS Marketplace
 Alibaba Cloud
Identify and remediate misconfigurations and high-risk settings for Alibaba Cloud with Aqua’s Cloud Security Posture Management, and secure Alibaba Cloud Container Service for Kubernetes infrastructure and workloads with host scanning, assurance policies and run time protection.
 Google Kubernetes Engine (GKE)
Protect cloud native workloads on GKE with full lifecycle security controls, including image scanning, secrets management, and runtime security at scale.
Get Aqua from GCP Marketplace
 Google Cloud Platform
Protect cloud native workloads running on Google Kubernetes Engine (GKE) from development to production, deploy as a Kubernetes App from the GCP Marketplace.
Learn More
 IBM Cloud
Protect cloud native workloads running on IBM Cloud Kubernetes Service and IBM Cloud Private, from development to production, at enterprise scale.
Learn More
 Microsoft Azure
Protect cloud native workloads running on Azure from development to production, including Azure Container Service (AKS), Azure Container Instances (ACI) and Azure Functions.
Learn More
 Rancher
Protect cloud native workloads on Rancher with full lifecycle security controls that include image scanning, secrets management, and runtime security at scale.
 Red Hat OpenShift
Protect cloud native workloads on Red Hat OpenShift with full lifecycle security controls that include image scanning, secrets management, and runtime security at scale.
Learn More
 ServiceNow
Orchestrate incident management responses based on Aqua Security findings with automated ServiceNow integration. Leverage Aqua Response Policies for event notifications to direct and manage via ServiceNow workflows.
Learn More
Posture management continuously assesses the configuration of cloud and Kubernetes environments against security best practices and compliance frameworks. Cloud security posture management (CSPM) covers cloud accounts and services, and Kubernetes security posture management (KSPM) covers clusters, workloads and access. Aqua connects both to the running workloads they affect.
Agentless posture tools are useful for broad discovery, but configuration data alone cannot show what a running workload is doing. Aqua combines agentless cloud assessment with runtime intelligence from the Aqua Enforcer, so teams prioritize the misconfigurations that expose live applications and can control what runs.
KubeEnforcer is Aqua’s Kubernetes native control. It evaluates admission requests and resource changes as they occur, applies Aqua policy and custom OPA Rego rules and connects cluster, namespace, deployment and image context to workload protection.
Aqua maps cloud, Kubernetes, host and identity findings to frameworks including CIS Benchmarks, NIST, PCI DSS, HIPAA, GDPR, SOC 2 and FedRAMP. Continuous assessment shows that controls are operating in production, not only that a configuration was checked once.
Posture Management gives visibility into supported human and machine identities and their effective permissions, and uses that context in toxic combination analysis. It is not a full CIEM or identity governance platform.
See runtime control stop an attack the moment it tries to execute.